 Not connected, Your IP: 216.73.217.113
 Online: 49814 users - 703341 Mbit/s total BW

Staff
-
Content Count
12024 -
Joined
... -
Last visited
... -
Days Won
2215
Posts posted by Staff
-
-
40 minutes ago, hedgehoq said:I have reached the maximum 5-session limit, but in the client area the sessions are just duplicates from old ones no longer in use.
Is there a way to manually "kill" these sessions from the client area?
Hello!
This function is not available for WireGuard connections, but "dead connection slots", i.e. sessions without any successful handshake for 2 consecutive minutes, should be freed up within 2 minutes plus a slight delay due to backend operations and communications. If you have a ghost connection slot that is not freed up within 3-4 minutes please do not hesitate to open a ticket to let the support team investigate the matter.
Kind regards
-
15 hours ago, chimney sweep said:the Swedish servers are particularly slow for me.
Hello!
We're glad to inform you that infrastructural power up in Sweden will take place, probably throughout September and October.
15 hours ago, chimney sweep said:I remember having some less than ideal speeds with servers in Switzerland for a while. Today they are OK.
We're glad to know it!
Kind regards
chimney sweep reacted to this -
Hello!
The SHA-256 checksum published on our website is provided specifically to allow users who sideload Eddie to verify the APK they downloaded.
The APK is also cryptographically signed. The certificate fingerprint shown by apksigner can be used to verify the signing certificate of the APK, but the SHA-256 checksum published on our website is the reference we currently provide for independently verifying the downloaded APK.
We may consider publishing the signing certificate fingerprint as additional information, now that we publish the APK already signed.
Kind regards
-
7 hours ago, MarxBrother said:I didn't know that I could switch easily to X11. I did so, but with not enough success. Eddie's reaction is faster now, but it still takes about seven seconds just to highlight a server.
Hello!
Something else must be wrong because this does not seem to happen on a vanilla Debian 13 with KDE Plasma 5, we'll consult with developers. In the meantime can you please make sure that you have the latest Mono package available on the repositories?
7 hours ago, MarxBrother said:Any info about the release of the Mono-free version?
An alpha version (probably not ready for public testing) will be deployed for internal testing on mid-September. However, we can't still claim a definite date for a public alpha or beta version, we're sorry. If Eddie remains unusable, you can consider to run the AirVPN Suite, until a new Eddie version that gets rid of Mono comes out: https://airvpn.org/forums/topic/79336-airvpn-suite-resources/
The Suite offers more options such as per app traffic splitting, but it does not feature any GUI. Everything is driven from a command line interface.
7 hours ago, MarxBrother said:BTW, does it have any disadvantages to use X11 vs. Wayland?
Currently only advantages, as Wayland and its compositors are still problematic on Debian 13 and need improvements, while X.Org is rock solid. On Debian 12 Wayland is almost unusable so there's no competition.
7 hours ago, MarxBrother said:BTW, the support here is superb. And even on a sunday!

Kind regards
-
11 minutes ago, MarxBrother said:The problem exists also under an up to date Debian 13 and KDE Plasma 5.
Hello!
This may mean that Wayland is still a problem and actually our tests are on X.Org based machines. You should consider to switch to X.Org and check whether all the problems get resolved. On Debian 13 and 12, the normal way is to select the Plasma (X.Org) session from SDDM. If you perform the test, please let us know whether the problems get resolved or not:- Log out of Plasma. You do not need to reboot.
- At the SDDM login screen, select your user.
- Open the session menu, a button or icon near the lower-left corner.
- Choose Plasma (X11) or Plasma (X.Org).
- Log in.
- Run Eddie and check.
11 minutes ago, MarxBrother said:
I'd like to, but I don't know how. Can you explain to me?53 minutes ago, Staff said:Can you also tell us which compositor is used in your Plasma environment (in Plasma, this is typically KWin)?
On KDE Plasma 5 on Wayland, the compositor is normally KWin, running as kwin_wayland. Use these commands to confirm:
echo "$XDG_SESSION_TYPE"
If it prints:
wayland
check the compositor process:
ps -e | grep '[k]win_wayland'
If the output shows (also) kwin_wayland, the compositor is KWin. If not, just send us the whole output.
Kind regards
-
21 minutes ago, MarxBrother said:The user interface became painstaking slow. When I click on a server, it takes around 10 seconds before it is even selected. This makes it unusable.
Hello!
The GUI is mainly managed by Mono and this problem is not reproducible on our and our customers' Linux systems. Specifically, one of our testing systems is Debian 13 with KDE Plasma 5, and we don't see any problem at all. However, our DEs run on X.Org server, not on Wayland. Eddie and Mono may have various problems with Wayland on Debian 12, just like a lot of other applications have. You can consider to switch to X.Org.
Can you also tell us which compositor is used in your Plasma environment (in Plasma, this is typically KWin)?
Next Eddie GUI will not need Mono anymore and Wayland compatibility will be improved, but probably not on systems with archaic packages like Debian 12 (see below).
21 minutes ago, MarxBrother said:I am not willing to switch to Windows or Ubuntu or whatever for that.
But you can consider to upgrade to Debian 13. Debian 12 Wayland support was not ready for everyday use, while things improved on Debian 13. Also, Debian 12 regular security support ended on June 2026 and its kernel is very old, therefore upgrading to Debian 13 is in any case a good idea if possible. Also consider that Debian 13 is now the main development platform for Eddie Linux edition.
Kind regards
ByteBuccaneer reacted to this -
41 minutes ago, xero said:Anyone with similar problems or a solution?
Hello!
Please check here first, just in case:
https://airvpn.org/forums/topic/70164-linux-network-lock-and-firewalld/
Kind regards
-
Hello!
@Flexion informed the support team that the problem was caused by the specific configuration of a private tracker limiting downloads for new users for a certain period of time. Therefore, "non-priority user" will have trouble in seeding. 🙄
Case closed. 😁
Kind regards -
5 hours ago, Harold99_0 said:Yeah, that fixed me. All the servers are back. I couldn't connect through WireGuard though. I had to use openVPN. As long as that provides me the same protection though I'm fine.
Hello!
It's expected, unfortunately. Eddie includes the latest WireGuard version which requires macOS 12 Monterey or higher versions. The privacy protection offered by OpenVPN, anyway, is slightly higher than that offered by WireGuard. Furthermore there is no WireGuard kernel module for macOS so the performance gain you have on other systems from saving kernel space↔userspace crossing and packet-buffer movements is lost.
Kind regards
Harold99_0 reacted to this -
7 hours ago, nopcode85 said:Cannot upgrade, newer versions do not work. See other posts on this and related access failures.
Hello!
In this case you need to run either the AirVPN Suite, WireGuard or OpenVPN. Please see here:
https://airvpn.org/forums/topic/79336-airvpn-suite-resources
If you opt for WireGuard or OpenVPN native software, our Configuration Generator, available on your AirVPN account "Client Area", can generate all the profiles you need.
Eddie Desktop edition runs on hundreds of distribution, but it is objectively difficult to offer total compatibility with all the 500+ actively maintained ones. However, the supported amount increases. For example, in this last version Eddie offers enhanced compatibility with distributions based on SysV-style init (before this version only the Suite had total compatibility with init based distros).
Kind regards
-
Hello!
Please upgrade, your Eddie version is too many years old. See also:
https://airvpn.org/forums/topic/81119-limited-server-access/
@yeshi
On PCLinuxOS please try the tarball.
Kind regards
-
50 minutes ago, _Bob_ said:checked the white list in my firewall. Turned out "Eddie-CLI-Elevated-Service.exe" was not there
Solved!
Kind regards
-
Eddie 2.26.2 Desktop Edition released
Hello!
We're very glad to inform you that a new stable release of Eddie is now available for Linux (various ARM based architectures included, making it compatible with several Raspberry Pi systems), macOS, Windows.
Special thanks to all the beta testers, whose invaluable contributions and suggestions in the last months have helped developers fix several bugs and improve the overall stability of the software.
Eddie is a free and open source (GPLv3) OpenVPN GUI and CLI by AirVPN with many additional features such as:- traffic leaks prevention via packet filtering rules
- DNS handling
- optional connections over Tor or a generic proxy
- customizable events
- traffic splitting on a destination IP address or host name basis
- complete and swift integration with AirVPN infrastructure with OpenVPN and WireGuard
- white and black lists of VPN servers
- ability to support IPv4, IPv6 and IPv6 over IPv4
- support to Linux systems based on systemd and SysV-style init
This version includes bug fixes and security improvements as well as OpenVPN, WireGuard and libraries updates.
A new Eddie UI is in the works. We know we’ve been promising that for a long time, but development is well along. Stay tuned.Operating and architectural notes
Eddie GUI and CLI run with normal user privileges, while a "backend" binary, which communicates to the user interface with authentication, gains root/administrator privileges, with important security safeguards in place featured in this new version:- strict parsing is enforced before passing a profile to OpenVPN in order to block insecure OpenVPN directives
- fix for CVE-2025-14979
- backend hardened authentication of client commands
- hardened security for sensitive operations
- client memory usage protection through limitation of client helper replies
- general cleanup
Furthermore:- external system binaries which need superuser privileges (examples: openvpn, iptables, hummingbird) will not be launched if they do not belong to a superuser.
- Eddie events are not run with superuser privileges: instead of trusting blindly user's responsibility and care when dealing with events, the user is required to explicitly operate to run something with high privileges, if strictly necessary
Please consult the changelog for a more detailed and exhaustive list.
Backend binary is written in C++ on all systems (Windows included), making the whole application faster.
Settings, certificates and keys of your account stored on your mass storage can optionally be encrypted on all systems either with a Master Password or in a system key-chain if available.
Download Eddie 2.26.2
Eddie 2.26.2 can be downloaded here:
https://airvpn.org/linux - Linux version (several architectures and various distribution specific packages for easier installation)
https://airvpn.org/macos - Mac version
https://airvpn.org/windows - Windows version
Eddie is free and open source software released under GPLv3. Source code is available on GitHub: https://github.com/AirVPN/Eddie
Complete changelog can be found here.
Kind regards & datalove
AirVPN Staff -
1 hour ago, stookie said:Thank you for that reply, but my query was about Mac High Sierra — can you tell me if I can run Eddie 2.24.6 using that version of Mac OS? I don't want to completely mess up my connection if it's not possible.
Hello!
We're sorry, Eddie 2.24.6 requires macOS Mojave or higher versions. If your Mac is Intel based you can run Hummingbird 2.1.0 (Hummingbird is optimized for Apple Silicon Mx too, but with this CPU Hummingbird requires Mojave or higher versions). Alternatively, you can consider OpenVPN Connect, or Tunnelblick 3.8.8g, but this Tunnelblick version contains serious vulnerabilities: https://www.tunnelblick.net/downloadsDeprecated.html
Kind regards
-
1 hour ago, panelbeater said:I can't use 2.24.6 on my brand new Macbook running Tahoe as all the workarounds to stop it continuously connecting and disconnecting failed, so have to use 2.21.8.
Hello!
On macOS Tahoe you can run Eddie 2.26 (now available on all download pages as a stable release) or Hummingbird 2.1.0 (on top of any other non-AirVPN software of course, such as WireGuard, Tunnelblick etc.).
QuoteMy IMac, which won't go higher than Catalinia is also on 2.21.8 and is showing the same problem.
On macOS Catalina you can run Eddie 2.24.6, Hummingbird 2.1.0, Tunnelblick etc. We will verify with developers compatibility between Eddie 2.26 and Catalina and will let you know.
Quoteall older operating systems, that can't run 2.24.6, will be cut off from using your service
Obviously not. At present, any system capable of running WireGuard, AmneziaWG 0.2.15, or OpenVPN 2.4 and later can connect to our service as usual.
The most significant change following the deployment of DCO across our infrastructure is the discontinuation of support for OpenVPN 2.3 and earlier versions.
Considering that OpenVPN 2.3 was released in 2013 and OpenVPN 2.4 in 2017, AirVPN’s continued support for such long-standing version demonstrates its strong commitment to backward compatibility - provided that maintaining compatibility does not compromise security or hinder the proper evolution of the service.
Kind regards
-
10 hours ago, Lucan Niewhoner said:what's causing these throttles that doesn't result in a "Status Log" issue.
Hello!
In a couple of cases, DDoS / flood attack was ongoing but was mitigated and caused no packet loss or other critical issue that could be detected by the monitoring system. However, they caused some problem: bandwidth impact and inability to communicate with the backend servers, which in turn did not have data to fill all the stats. However, the monitoring system did not put the server on "limited access" or "closed access" and did not log the issue mainly because IPv4 and IPv6 addresses were all reachable with no packet loss and not other failures were detected.
Another case is simply congestion on any upstream. Although we have a guaranteed bandwidth inside the datacenter and on interconnection with the main IP transit, some routes can be occasionally congested, even when this problem is not caused by the datacenter network and/or by the transit provider. However, this is a rare case, whereas flood attacks are more common throughout the whole infrastructure.
The last case is occasional. When the server needs an urgent kernel upgrade, it will be rebooted, and therefore will go completely down for a couple of minutes. However, this event is always recorded on the stats as it causes 100% packet loss on all addresses.
Kind regards
-
@bilis
@riotamus
@Harold99_0
@sebalpatine
@zeedatrup
@Veep Peep
Hello!
A plausible explanation is that you're running an obsolete Eddie Desktop edition version. Eddie filters out servers whose connection mode is not compatible with your system setup. For example, as DCO support is completed throughout the whole infrastructure, an old Eddie version not supporting WireGuard and running an OpenVPN version 2.3.x will be unable to find a suitable server.
Please upgrade your Eddie Desktop edition and report back at your convenience.
If you are not running Eddie Desktop edition, please specify the software you're running.
Kind regards
-
18 hours ago, moving shadow said:I gotta say, the service is really degrading lately, especially the Tzulo servers that deliver the better speeds. Castula is down AGAIN with packet loss. What the hell is going on here? It's becoming REALLY unreliable -- too unreliable to even have a self hosted server because the servers keep going down randomly for hours at a time for no rhyme or reason
Hello!
First of all please respect the netiquette or you will be moderated.
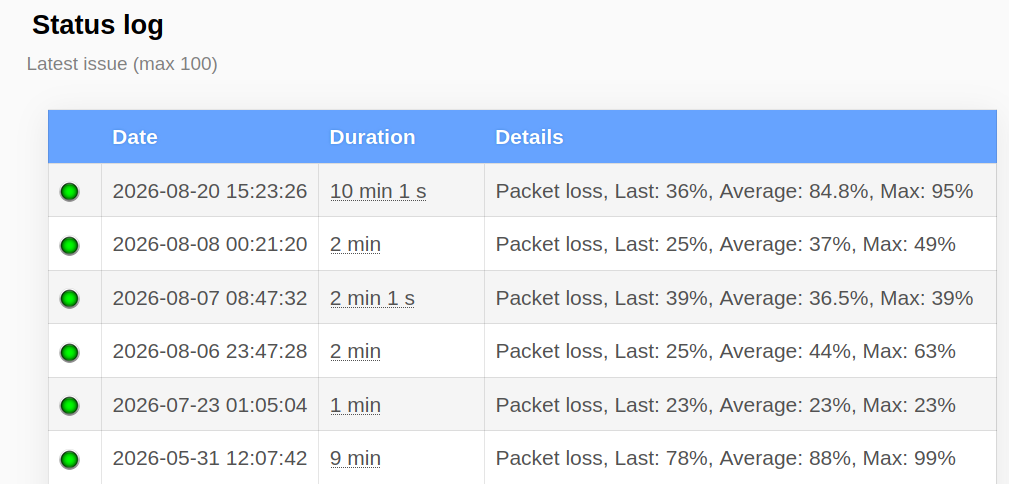
You provided inaccurate information about Castula. Here below a screenshot (from the public real time servers monitor) with the recent history of the problems it had. As you can see, such problems were not critical. Packet loss occurred for a very limited time, a matter of minutes, and sporadically: no events in June, only one event in July, not impacting events on August. Note how solid and reliable Castula is.
Also note that the packet loss is recorded as a weighted average of ping from VPN server to various testing servers in different locations, and from those testing servers to the VPN server. Thus, the outcome is reliable but a small probability that the problem affects the testing servers, or any hop in-between, and not the VPN server, remains. The same can be said for each VPN client node: if a client loses packets to or from a VPN server, the problem is not necessarily only on the VPN server side.
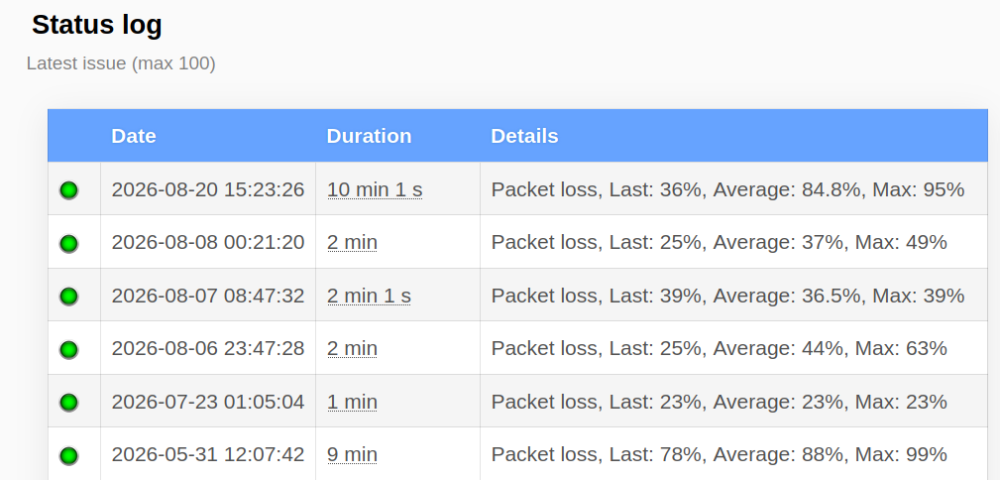
Uptime is more than 99.5% with Tzulo servers. Flood attacks may happen and can alter the normal uptime, but after 1 year the uptime remains good and the servers are solid.
You use AirVPN for self hosted servers, although this is not the purpose of the service. For self hosted servers you may need a dedicated server or your own VPS, especially if you want more than 99.5% uptime and all inbound ports available. Using AirVPN for hosting purposes is possible but questionable. Even if AirVPN offers remote inbound port forwarding, AirVPN is not a hosting provider and you can't expect for the current price the same performance you have with a dedicated or virtual server with business lines that you operate exclusively.
Also note that downtime due to server maintenance (especially for kernel upgrades) is another factor that you can't manage by yourself and that makes AirVPN not suitable for hosting purposes if you pretend the uptime of a hosting provider. We can upgrade and reboot the servers when necessary especially for security reasons and best practice.
With all the above said, we are constantly striving to improve our service; however, limitations may arise when it is used for purposes for which it was not designed.
Kind regards
DeepAnger and PWolverine reacted to this -
Hello!
We're very glad to inform you that a new 10 Gbit/s full duplex server located in Los Angeles, California, is available: Flegetonte.
The AirVPN client will show automatically the new server; if you use any other OpenVPN or WireGuard client you can generate all the files to access it through our configuration/certificates/key generator (menu "Client Area"->"Config generator").
The server accepts connections on ports 53, 80, 443, 1194, 2018 UDP and TCP for OpenVPN and ports 1637, 47107 and 51820 UDP for WireGuard.
Flegetonte supports OpenVPN over SSL and OpenVPN over SSH, TLS 1.3, OpenVPN tls-crypt and WireGuard.
Full IPv6 support is included as well.
As usual no traffic limits, no logs, no discrimination on protocols and hardened security against various attacks with separate entry and exit-IP addresses.
You can check the status as usual in our real time servers monitor , by clicking the server name. Direct link: https://airvpn.org/servers/Flegetonte
Do not hesitate to contact us for any information or issue.
Kind regards & datalove
AirVPN Staff

-
17 hours ago, Catacomb5442 said:AirVPN tile does not work with AmneziaWG. Otherwise: awesome! Great protocol. Much faster than WG where I live.
Hello!
Thank you! Can you please describe all the steps you perform to reproduce the problem? Can you also add the app's log generated after you have reproduced the problem? In the "Log" view please tap the paper plane icon and send the link that the app will give you back.
Kind regards
-
8 hours ago, map525 said:I can't see any of the servers in Los Angeles in Eddie. I tried logging out and back in and deleting the default.profile file but to no avail. I am running on Windows 10.
Hello!
Which Eddie version are you running? Can you also generate a system report and send us a link to it? https://airvpn.org/forums/topic/50663-youve-been-asked-for-a-support-filesystem-report-–-heres-what-to-do/
Kind regards
-
23 hours ago, Tommie said:Why then can I run the Wireguard.app itself (1.0.15) with no problem using AirVPN config generator? Totally stable.
Hello!
Because it's not the latest version, which is 1.0.16, and which requires macOS 12 or higher version. https://apps.apple.com/us/app/wireguard/id1451685025?mt=12
Kind regards
-
On 7/31/2026 at 1:08 PM, Janice Redfern said:Develop opensource clients that allow other VPN providers to just plugin their details (login server or whatever)
Hello!
This is an interesting smearing message that occasionally comes out, trying to exploit the forum we keep open for the community, for some hidden purpose or, we guess, just for hate. You can easily verify that every defect mentioned by the OP is either false or distorted. A community moderator provided some corrections that disprove the OP's claim, here we would like to add just three remarks on subjects we care about: interoperability with other VPN services, infrastructure stability and how good our remote port forwarding system is. We also want to quickly make you aware that the OP never opened a ticket for professional support, so he/she was probably not interested in a solution of his/her problems, but maybe only in building a case based on false or fabricated premises.
1. Eddie Android edition, AirVPN Suite and Eddie Desktop edition allow connections to any VPN supporting either OpenVPN or WireGuard through the most standardized method that can exist, the supported profile for each VPN application (much better than any API, especially when it does not exist on most VPN services).
2. Over the past 16 years AirVPN infrastructure constantly evolved toward more stability and speed, it's all in the records.
In AirVPN we have had and we have users connected CONTINUOUSLY for SEVERAL MONTHS. Enough for connection stability? 😉 We could have even longer periods, if it wasn't for the necessity to reboot a server periodically for kernel upgrades.
3. Implementing remote inbound port forwarding over a VPN by having the VPN server use UPnP/NAT-PMP/PCP to dynamically open ports on behalf of clients is generally considered a poor architectural choice because:- UPnP was designed for trusted, local networks
- No authentication in classic UPnP IGD exists
- Race conditions in a large infrastructure like AirVPN's one becomes an architectural problem
- UPnP would make "hot change" and other interesting features appreciated by AirVPN customers impossible
- Privilege escalation. UPnP used outside a local network facilitates various exploits including privilege escalation.
- The VPN server already controls firewall rules, NAT, routing and connection tracking. Using UPnP as an intermediary adds another protocol layer rather than configuring those systems directly. This depends on your design philosophy, but at the moment management does not see favorably functionality duplication.
Kind regards
-
@fishbasketballaries
Hello!
The error means that Android is refusing to install the APK because an app with the same package name (org.airvpn.eddie) is already installed, but it was signed with a different certificate.This is perfectly possible as the new APK has been signed with our official Google developers signing keys to make life easier for the imminent, new restrictions against side load, while the previous ones were not signed with them. Please uninstall the previous packageadb uninstall org.airvpn.eddie
and then install the new APK.
Kind regards

ANSWERED Manually ending a session from client area
in Troubleshooting and Problems
Posted ...
Hello!
Not necessarily. On which exact OS do you see this behavior? Which software do you run for AmneziaWG connections? The proliferation of tun interfaces must not occur, unless you explicitly try multiple concurrent connections. In such a case you will see multiple active connection slots on your AirVPN client area, yes.
Kind regards